Prevent $1M Breaches: Software Threat Modeling
True software security begins during design, not with firewalls. Threat modeling identifies weaknesses long before a single line of code is written, saving costly fixes.
Security Starts Early: Design It In
Software security often brings to mind firewalls, complex passwords, or antivirus programs. These are important, but true security begins much earlier. It starts long before anyone writes a single line of code. It begins before a system even goes live.
Security starts during design. That’s where Software Security Threat Modeling helps. Threat modeling identifies weaknesses. It finds them before they become expensive problems.
What threat modeling does
Microsoft introduced the STRIDE model in 2002. It was a significant advancement. Threat modeling teaches you to think like an attacker. This is a vital ability. It helps developers and security teams find weaknesses early, before they cause real trouble. This process works for any software: web apps, mobile apps, or cloud services.
Imagine designing a house. You don’t wait until it’s built to think about burglars. Instead, you plan for strong locks, secure windows, and alarms during the blueprint stage. Threat modeling does this for software. It checks the system’s blueprint. It finds where attacks might happen.
Who’s involved? Software architects, developers, and security analysts. They work together. They scrutinize system designs before writing any code. What do they scrutinize? The system itself: its data flows, components, and user interactions. When? Early in the development lifecycle, ideally during design.
How teams find weaknesses
Threat modeling isn’t guesswork. It uses proven methods. These frameworks systematically analyze software. Two main ones are STRIDE and PASTA. They help teams ask the right questions.
Microsoft’s STRIDE model breaks threats into six categories, one for each letter. S is for Spoofing: An attacker pretends to be someone else. T is for Tampering: An attacker modifies data.
R is for Repudiation: An attacker denies doing something. I means Information Disclosure: Someone gets unauthorized access to sensitive data. D is for Denial of Service: It stops legitimate users from accessing a system. Finally, E is for Elevation of Privilege: An attacker gains higher access rights. Teams use STRIDE to check their system for each threat type.
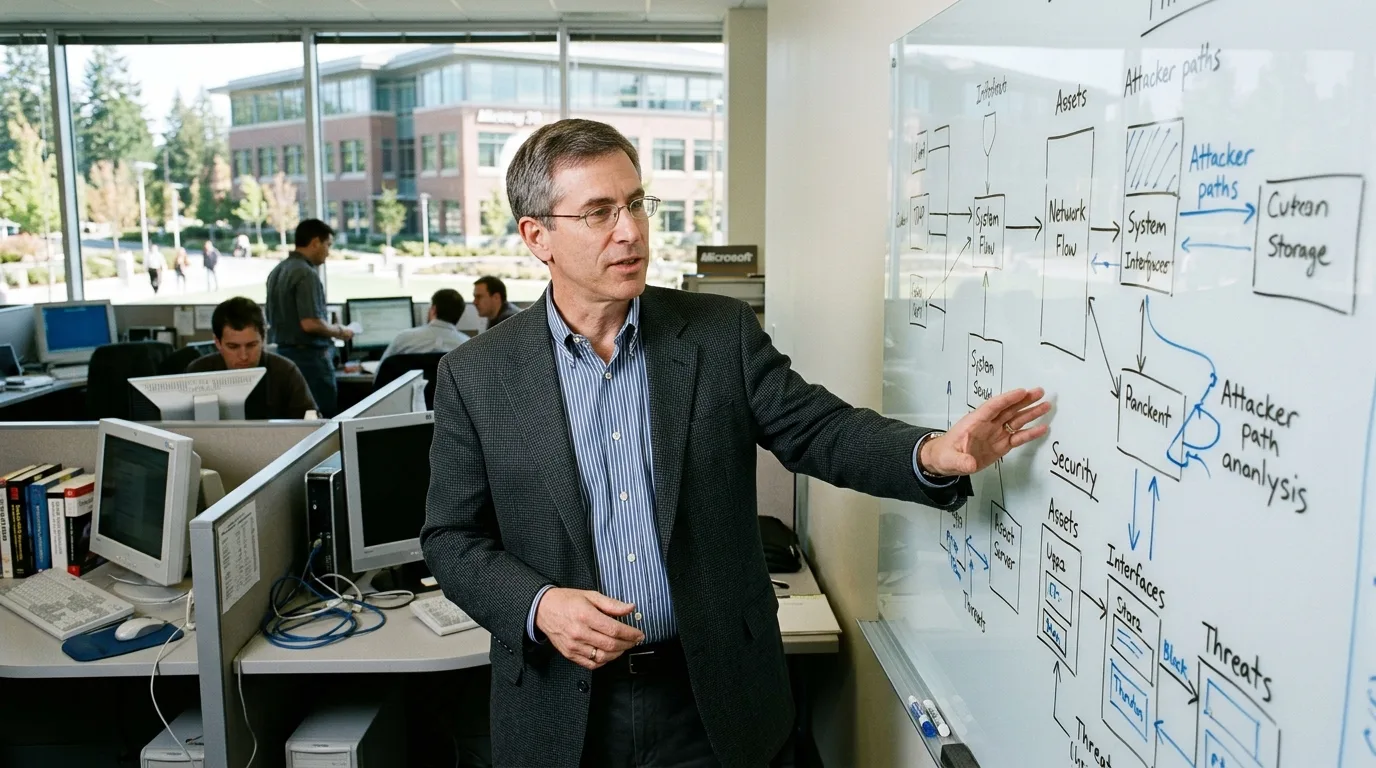
Loren Kohnfelder, a distinguished engineer at Microsoft, was instrumental in the development of the STRIDE threat modeling framework in the early 2000s. His pioneering work helped establish foundational principles for identifying and mitigating security weaknesses during software design. (AI-generated illustration)
Another method is PASTA, the Process for Attack Simulation and Threat Analysis. Tony Uceda-Velez and Marco M. Morana introduced it. PASTA is a seven-step, risk-focused method – meaning it ties everything back to real-world impact. It starts with business context. It identifies technical assets. Then it breaks down the application.
It simulates attacks. Finally, it evaluates risks. PASTA is a thorough method. It connects technical weaknesses to business impact. It prioritizes fixes based on real risk. This connects security with business goals.
Why early security saves money
An IBM study from 2011 showed a simple, brutal truth: fixing defects later costs far more. A bug found during design costs pennies. That same bug costs dollars during testing. And it costs hundreds or thousands after deployment. Threat modeling applies this “shift-left” principle. It catches issues early, saving you a fortune.
Take a bank, for instance. A major bank, without consistent threat modeling, built a new mobile app. They found a critical flaw late in testing. An attacker could bypass login under certain network conditions. This meant redesigning the login module. It delayed the launch by two months. The delay and rework cost over $1 million.
Threat modeling stops these problems. It makes dev and security teams work better together. Developers understand security risks better. Security analysts grasp the system’s architecture. This shared knowledge builds more secure software from the start. It cuts down on expensive post-release fixes.
Threat modeling also helps meet compliance. Regulations like GDPR or HIPAA demand privacy and protect data. Find data flow risks early, and organizations can bake in controls. This ensures legal standards. It also avoids big fines. IBM’s 2023 report says the average data breach cost $4.45 million. Early security is simply good business.
Threat modeling in modern development
Adding threat modeling to agile development is tough. Agile wants speed and quick releases. Long security reviews slow things down. Modern methods add threat modeling in a way that makes it continuous.
Tony Uceda-Velez and Marco M. Morana are the creators of PASTA, the Process for Attack Simulation and Threat Analysis. This seven-step, risk-focused method ties technical weaknesses to business impact, helping organizations prioritize security fixes based on real-world risk. (AI-generated illustration)
Teams do small threat models for each new feature. They do this during sprint planning. They use simple tools and templates. This keeps it quick and efficient. OWASP, a global group improving software security, backs this. They offer resources and frameworks. These help teams adopt continuous threat modeling.
Automation is growing too. Tools can analyze code. They find threat vectors. They can even suggest STRIDE threats. This cuts manual effort. It speeds up initial analysis. Security expert Adam Shostack, author of “Threat Modeling: Designing for Security,” says automation helps scale threat modeling. It makes it accessible to more teams.
What’s next: evolving threats and smarter solutions
Cybersecurity changes fast. New tech brings new risks. AI and machine learning (ML) systems are more complex. Their unique weaknesses need special threat modeling. Quantum computing, still emerging, promises to break current encryption. This will need entirely new security approaches.
Large language models (LLMs) in AI apps have unique threats. We’re talking prompt injection, data poisoning, and model inversion. Traditional threat models must adapt. They must handle these new attack surfaces, which are unlike anything we’ve seen before. Researchers are developing new frameworks for AI security. This ensures these powerful tools don’t become huge problems down the line.
Threat modeling will keep evolving. It will become a more fundamental part of software development. It will use AI to find weaknesses. This early approach will remain vital. It keeps up with advancing threats. It builds safer, stronger software for everyone.
FAQs
Who should be involved in threat modeling? A cross-functional team should participate. This means architects, developers, security analysts, and product managers. Different viewpoints help find more threats.
When is the best time to perform threat modeling? The best time is early in software development. This means during the design and architecture phases. It builds in security, instead of adding it later.
Is threat modeling only for large, complex systems? No, it helps systems of all sizes. Even small apps can have serious weaknesses. A quick, light threat model is always worth it.
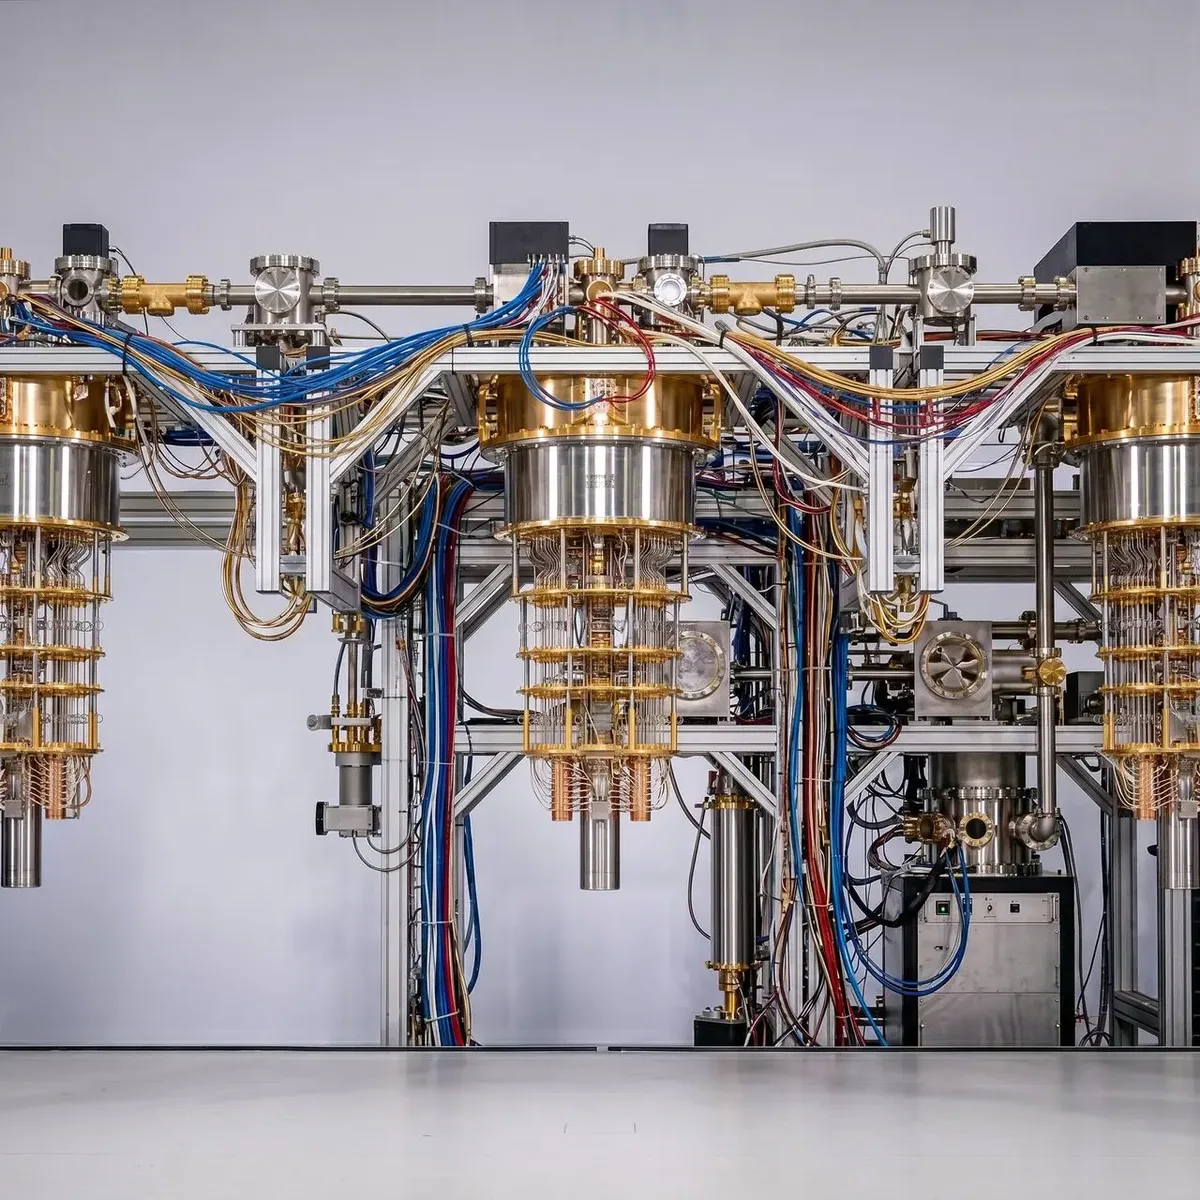
Quantum computing, an emerging technology, poses a significant future threat to current encryption methods, necessitating entirely new security approaches and advanced threat modeling. These complex machines often feature distinctive, cryogenic hardware, such as dilution refrigerators, to maintain the extremely low temperatures required for their operation. (Source: quantumzeitgeist.com)
What’s the first step to start threat modeling a new project? First, define the system’s scope and purpose. Then, create a data flow diagram. This shows how data moves through the app.
You might also like:
👉 WannaCry 2017: The Cyberattack That Crippled UK Hospitals